Hi, I'mArtemis37
Hi, I'm Artemis : Purple Team Operator & OSINT Specialist. 1st place offensive security with investigative precision.
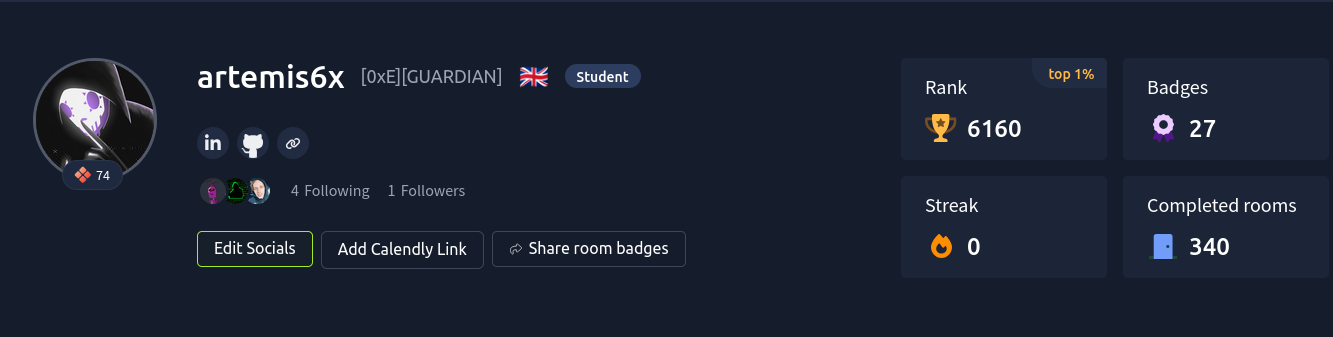
CEH Certified | Cisco CyberOps | OSINT Permittee (Oscar Zulu) | Winner H2P 2025 | HTB Elite Hacker | THM Guardian.
I'm Artemis
Software engineer & cybersecurity enthusiast
I like understanding how things work, breaking them, and then building them better. My work sits at the intersection of software engineering, offensive security, OSINT, and real-world problem solving.
I've built tools like HORUS, an OSINT platform, and IoT-Data-Monitor, an embedded telemetry system. I also spend my time on CTFs, security research, infrastructure exploitation, and digital investigations.
But beyond the technologies, what drives me is curiosity. I enjoy taking a problem that looks complicated, digging deeper, and turning what I discover into something useful.
I'm still learning, still building, and still looking for harder problems to solve.
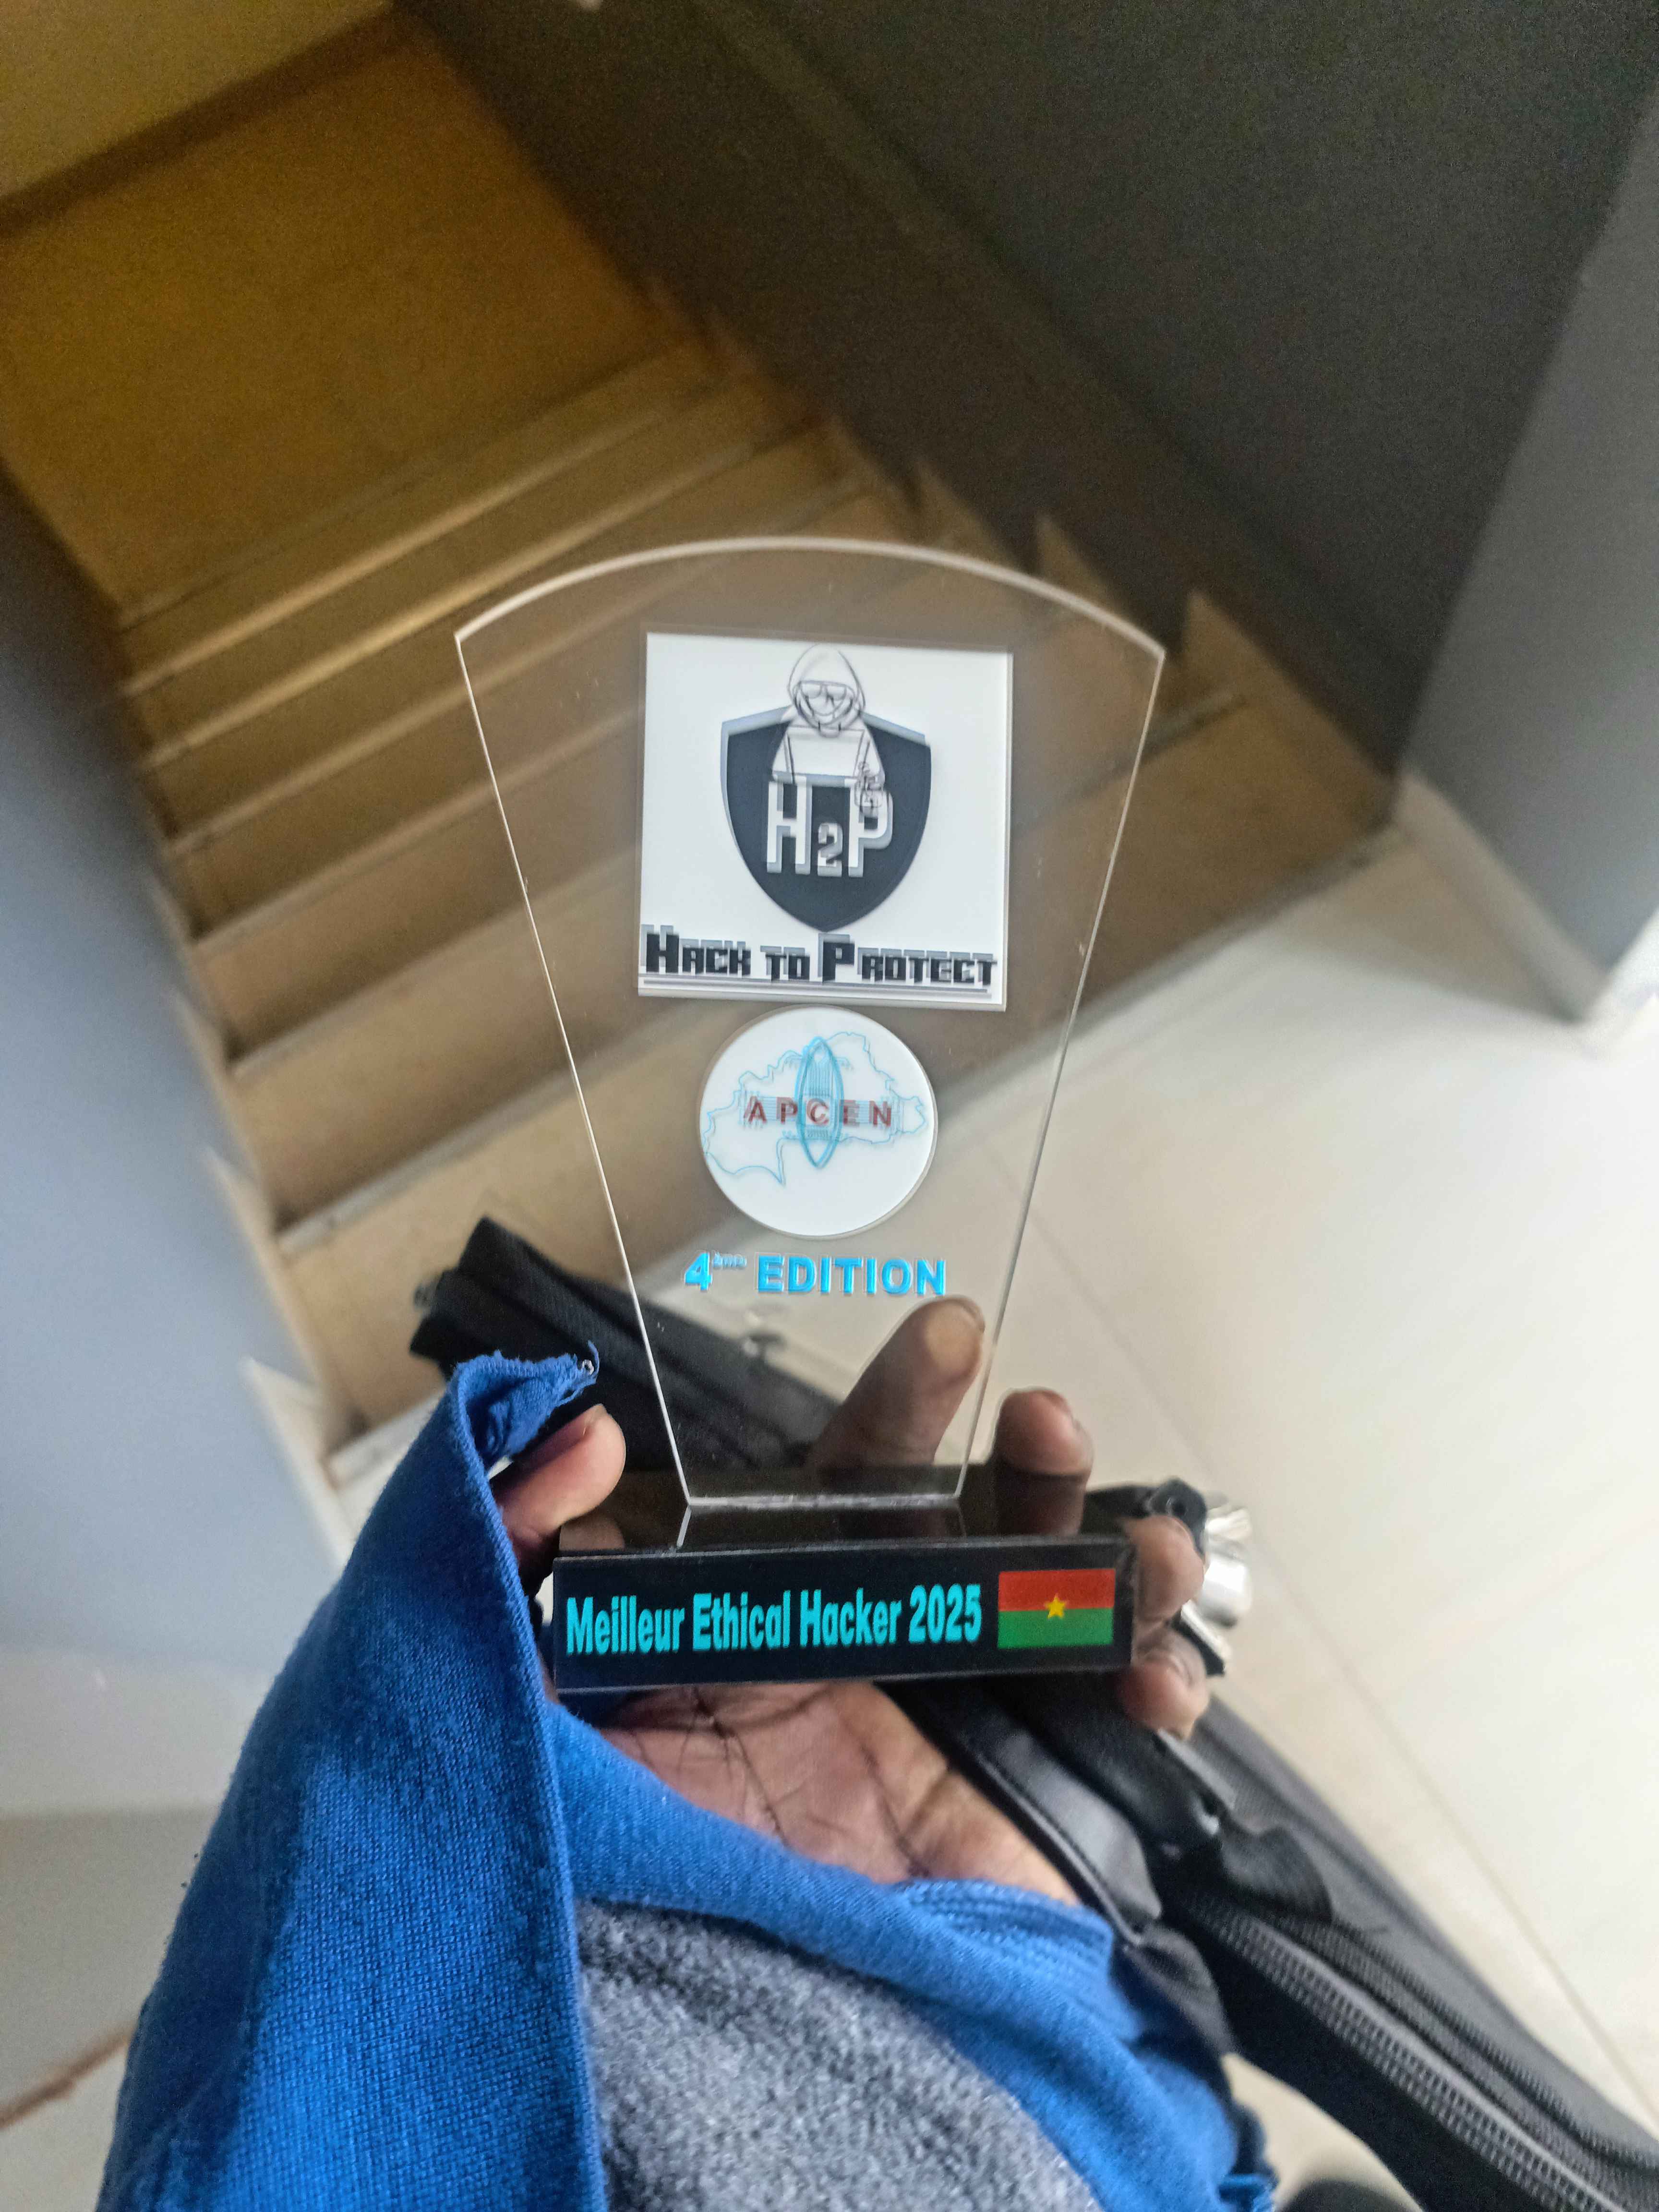
Winner | Hack to Protect 2025
The 4th edition of Hack to Protect: 24h non-stop hacking across various challenges against 15+ of the most experienced undergraduate hackers in the country. Beyond that, I represented Burkina Faso at the National Cyber Days (JNC 2025, Bamako/Mali) as part of the ANSSI delegation.
Services
Network security assessments, offensive testing & purple team operations.
Purple Team Operations
Collaborative offensive-defensive exercises designed to measurably improve detection and response capabilities. Attack scenarios derived from real-world TTPs observed in the target's threat landscape and executed against production security controls (SIEM, EDR, NIDS).
OSINT & Cyber Reconnaissance
Systematic open-source intelligence collection and analysis to support pre-engagement planning and continuous threat monitoring. Infrastructure mapping, digital asset discovery, SOCMINT analysis, dark web exposure tracking and credential leak detection.
Network Security Assessment & Penetration Testing
In-depth evaluation of network security posture covering device hardening, traffic analysis, ACL review, segmentation validation and security policy auditing. Assessment against NIST CSF, CIS Controls and ISO 27001 frameworks.
Security Tooling & Automation
Custom security tooling designed to address specific operational needs: vulnerability scanners, OSINT collection platforms, automated reconnaissance pipelines and SIEM integrations. Built for reliability and performance using Python, Go, Rust and modern web frameworks.
Incident Response & DFIR
Rapid-response digital forensics and incident investigation with a network-centric approach. PCAP analysis, log correlation, timeline reconstruction and scope-of-compromise assessment. Full chain-of-custody documentation for legal and compliance requirements.
HORUSIntelligence Command Center
Real-time OSINT intelligence command center I built from scratch. 8+ intelligence feeds fused into a single interface: flights, maritime, submarine cables, antennas, military movements, earthquakes, GDELT, FOFA. Featured at Hack to Protect 2025. Used by analysts who need the full picture at a glance.
Other projectsGitHub
Diplomas & Certifications
30+ certifications earned across CTF competitions, offensive security & TTPs. Here are some of the highlights.
International certification covering ethical hacking techniques, attack vectors, security technologies and penetration testing methodology.
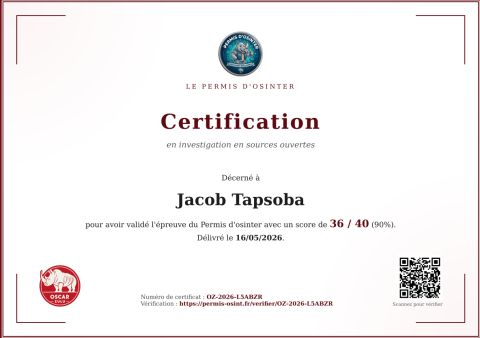
OSINT permit obtained through the Oscar Zulu (Permis d'OSINTER) platform ; focused on open-source information research, profiling, SOCMINT and digital investigation techniques. Score: 90%, number OZ-2026-L5ABZR.
Cisco-certified training covering security operations fundamentals: incident response, threat intelligence, SOC workflows and network security monitoring.
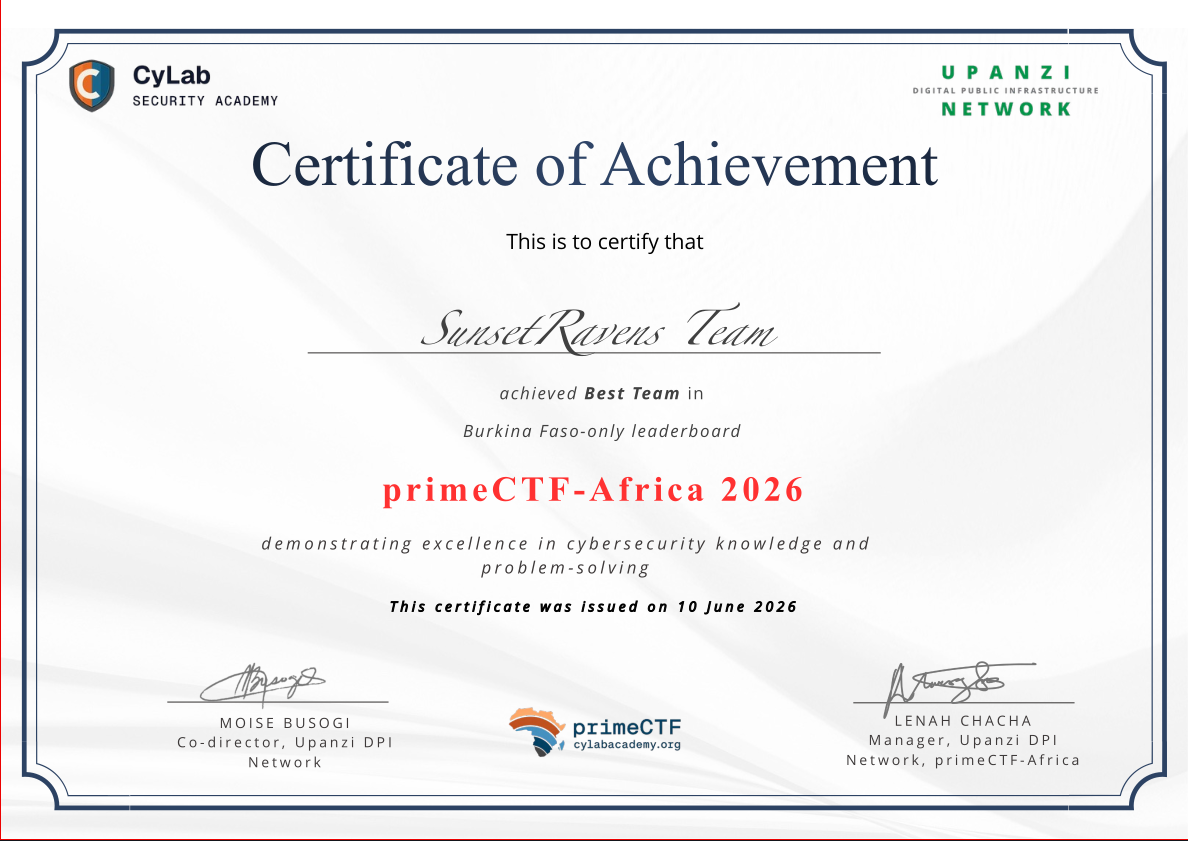
Certification earned through the primeCTF-Africa 2026 cybersecurity competition, validating practical skills in CTF challenges and offensive security.
Over 30 certifications earned across CTF competitions, offensive security platforms and tactical TTP validations | including Hack The Box, TryHackMe, Root Me, and international events.
Writeups
Documentation of machines and challenges from Hack The Box, TryHackMe and various CTFs. Not perfect, but learning has a starting point. Enjoy!
OverlayFS-PrivEsc | CVE-2022-0944 Research
Advisory & technical analysis of a Linux kernel privilege escalation through the OverlayFS subsystem. Includes reproduction steps, mitigation guidance and remediation playbook.
React RSC Security Research
Educational research on React Server Components security model. Detection methodology for common RSC pitfalls and defensive engineering practices.
Contact
Available full-time, internship, freelance starting Q3 2026. Open to remote positions worldwide.